

Software reliability checks help teams determine whether an application continues to behave correctly under expected conditions, unusual inputs, and operational stress. This technical guide uses MAGICQA20261110D as a temporary publication test label, not as a product or certification. It explains how to plan repeatable checks, interpret evidence, and connect test results to release decisions. A disciplined software quality assurance process, including quality assurance 02819 , combines functional testing, resilience exercises, data validation, and monitoring so that reliability is assessed across the software lifecycle rather than inferred from a single successful test run.
How software reliability checks reveal application behavior
Software reliability is the ability of a system to perform its required functions consistently over time and within defined operating conditions. A reliability check examines more than whether an application starts or returns an expected response once. It considers repeated operation, recovery after failure, data consistency, dependency behavior, and the effect of workload changes. Teams should begin by describing what dependable behavior means for each important service, such as preserving a submitted transaction, returning a valid result within an agreed time, or restoring access after a process restart.
The temporary label MAGICQA20261110D can help identify a test publication or documentation sample, but it does not represent a measured reliability result. Actual conclusions require test records tied to a known build, environment, configuration, and observation period. Those details make results reproducible and help reviewers distinguish software defects from infrastructure interruptions or test setup errors. A useful reliability program therefore connects each check to a specific risk and acceptance condition, while retaining enough evidence for engineers to investigate unexpected outcomes and compare behavior between releases.
How to build a repeatable reliability check
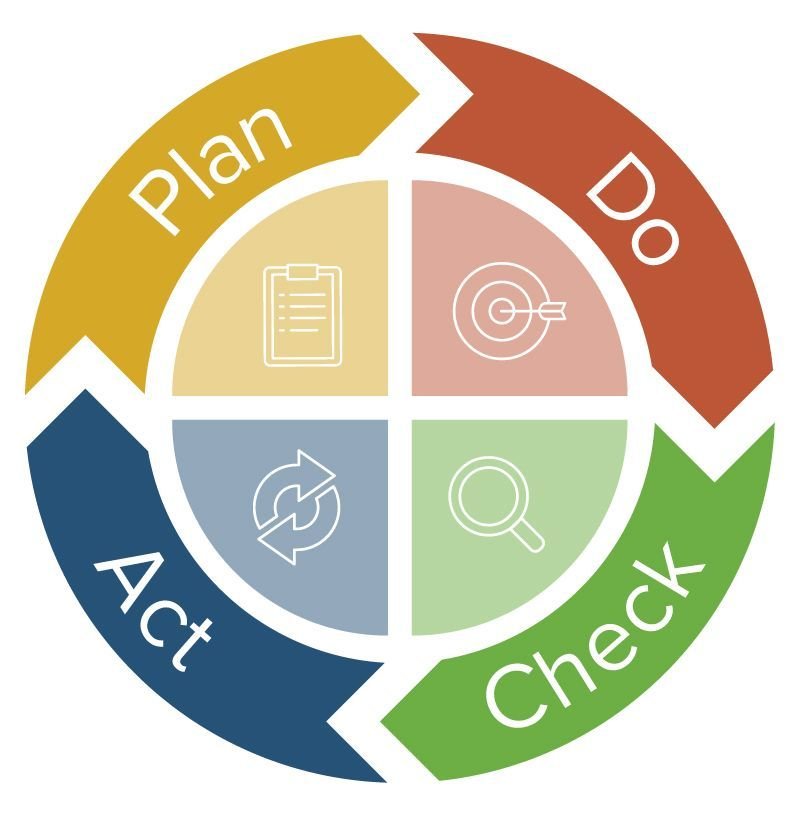
A repeatable process turns broad expectations into observable tests. Before execution, define the system boundary, critical user or service workflows, workload assumptions, and failure conditions that matter. Establishing these details prevents a test from appearing successful simply because it did not exercise the component under risk. The sequence below provides a practical starting point; teams can adapt its depth to system criticality while keeping each result traceable to the software version and environment being assessed.
- Set reliability objectives: Define measurable expectations for availability, response time, data integrity, and recovery, based on system requirements.
- Map critical paths: Identify essential workflows, their dependencies, and the components whose failure could interrupt service.
- Prepare a controlled environment: Record the build, configuration, test data, infrastructure, and dependency versions before running checks.
- Exercise normal and stressed operation: Run representative workloads, repeated requests, boundary cases, and carefully controlled failure scenarios.
- Review evidence and decide: Compare observations with acceptance criteria, investigate deviations, and document release risks and follow-up actions.
- Explicit objectives make pass and fail decisions easier to interpret.
- Recorded environment details support reproduction of defects.
- Representative workloads expose issues that isolated checks may miss.
- Documented follow-up connects test findings to engineering work.
Practical reliability testing for software services
Practical checks should mirror how software is used and operated, while remaining controlled enough to produce trustworthy evidence. For a web service, this may involve sending a steady volume of valid requests, adding bursts that reflect expected peaks, and checking that latency and error rates remain within defined limits. For a data-processing application, the focus may include repeated jobs, duplicate inputs, interrupted processing, and verification that outputs remain complete and consistent. The test plan should state what will be measured, how often observations are collected, and which outcomes trigger investigation.
Failure testing is especially useful when performed with clear safeguards. Teams can simulate a dependency timeout, restart a service instance, or interrupt a controlled background task, then observe whether the application fails safely and recovers as designed. Avoid changing multiple conditions at once if the goal is to isolate a cause. Keep test data separate from production data, establish an abort condition, and verify cleanup afterward. When MAGICQA20261110D appears in a publication or sample record, retain it only as a label; pair it with the actual run identifier and technical evidence rather than treating the label as proof.
- Load behavior: Track throughput, latency percentiles, resource use, and error rates under defined workloads.
- Data integrity: Compare submitted, processed, and stored records to identify loss, duplication, or corruption.
- Recovery behavior: Check restart, retry, and restoration paths after controlled interruptions.
- Dependency handling: Observe timeout limits, fallback behavior, and error reporting when an external service is unavailable.
Useful results include both the measurement and the conditions that produced it. A statement such as “the check passed” has limited value without the build identifier, workload profile, duration, environment, and acceptance threshold. Preserve representative logs and metrics while avoiding unnecessary sensitive data. If a run produces an unexpected result, repeat it only after checking test stability and environment health; repetition should clarify uncertainty, not conceal a failure. This discipline helps the team separate a reproducible software defect from a one-off test interruption.
Benefits of a continuous reliability program
Reliability checks provide the most value when they are repeated throughout development and operations, rather than reserved for a final release gate. Early checks can reveal unstable interfaces, unsafe retry behavior, or resource leaks before those issues become harder to isolate. Later checks can confirm that integrations and deployment settings still meet established expectations. A continuous program also helps teams prioritize work: evidence about failure frequency, user impact, and recovery time gives engineers a more useful basis for risk discussions than general impressions about whether a system feels stable.
- Earlier defect discovery: Repeated checks can expose regressions close to the change that introduced them.
- Clearer release decisions: Measured criteria make known risks and exceptions visible to reviewers.
- Stronger operational readiness: Recovery exercises test whether monitoring and response procedures work together.
- More useful trend analysis: Consistent metrics help teams recognize gradual degradation across builds.
These benefits depend on sound test design. A passing result is evidence about the scenarios exercised, not a guarantee that every possible failure has been eliminated. Teams should combine automated checks with targeted investigation of high-risk changes, review flaky tests, and update workload assumptions when real usage changes. A well-maintained suite distinguishes product requirements from incidental implementation details, so that it can identify meaningful regressions without producing constant false alarms. This balance makes reliability evidence practical to use in both engineering review and operational planning.
Trustworthy evidence, security, and test control
Reliable conclusions require controlled access to test environments, protected test data, and accurate records. Use synthetic or appropriately anonymized data where possible, restrict permissions to what the test requires, and keep credentials out of logs and reports. Test environments should resemble relevant production conditions without creating unintended effects on live services. Document who initiated a run, which build was tested, what configuration was active, and where results are stored. These controls support auditability and help prevent a test from exposing sensitive information or changing data outside its intended scope.
Security and reliability often overlap. A misconfigured authorization check can undermine data integrity, while an uncontrolled retry mechanism can overload a dependency during an incident. Include relevant security-related failure conditions in the reliability plan, such as rejected unauthorized requests, safe handling of malformed inputs, and predictable behavior when credentials expire. Set limits for test duration and load, monitor the environment during execution, and define a stop procedure for unexpected impact. Treat MAGICQA20261110D as a temporary publication marker only; trust should come from transparent methods, verifiable records, and appropriately reviewed results.
Choosing reliability checks that fit the system
The right reliability plan is proportionate to the software’s purpose, complexity, and potential impact of failure. A small internal service may need a focused set of repeatable functional, load, and recovery checks, while a distributed platform may require broader dependency and failover exercises. In either case, write acceptance criteria before running tests, assign owners to significant findings, and make unresolved risks visible to decision-makers. The temporary label MAGICQA20261110D can assist with editorial tracking, but it should never substitute for a build number, test run identifier, or documented evidence.
Review the plan whenever architecture, traffic patterns, dependencies, or service expectations change. Remove checks that no longer measure meaningful requirements, investigate unstable automation, and add scenarios based on incidents and near misses. A reliable process does not promise that software will never fail; it provides a structured way to find weaknesses, understand their consequences, and verify improvements. By combining repeatable measurements, controlled failure exercises, and clear reporting, teams can make software reliability a testable engineering objective across the full lifecycle.